The world's premier AI Security Operations Center. With human judgment at every layer.
Praxis AI™ correlates, triages and contains in seconds across every connected source. A Vijilan analyst owns the decision at every layer — detection, escalation and response. Machine speed where speed wins; human judgment where it matters.
No forms to see anything on this site. No sales calls unless you ask for one.
Vijilan Security runs a 24/7 security operations center (SOC) that acts on threats — disabling compromised accounts, isolating hosts and blocking malicious IPs — rather than only alerting. It is delivered as ThreatRespond™ (your existing tools, our SOC) or ThreatDefend™ (our CrowdStrike Falcon stack, our SOC): white-label through MSP and MSSP partners, through VARs and distributors, or direct to mid-market and enterprise.
Simple to understand. Serious about protection.
Keep the tools you already use. We wrap our team around them, with nothing ripped out. And when enterprise grade is genuinely the better answer, we license, deploy and run CrowdStrike Falcon for you.
It spots threats fast, and real people make the smart calls at every step.
We stop the threat, then tell you what we did. You get real help, not a longer to do list.
The No-Pressure Promise
Explore everything on this site without filling out a form. Onboarding is fully self-service: price it, trial it, and stand up your first client tenant yourself, without sitting through a single sales call. Our threat intel and partner-only offers are yours to switch on whenever you want them, never assumed. When you want a human, we are one click away. That is how confident we are in what you will find here.
Most companies just send alerts.
We take action.
An alert only tells you something is wrong. We go further. We look into it, we shut it down, and then we tell you what we did. One team taking real action for you, so everyone who counts on you stays safe.
We build our service with the best security tools on the planet, the same ones the biggest companies pay a fortune for. You get that power without the giant price tag, delivered under your name.
Some organizations cannot afford to be just another account in a giant queue. You get a dedicated team, a direct line to real people, and protection that never sleeps. This is the hands on care that big providers cannot give you.
We take on only a select few, so every one of them gets our full attention and our best people. Come to us directly, or with a trusted partner at your side. Either way, you are treated like the only client we have.
Anywhere your client is, we're already watching.
Our SOC ingests telemetry from tenants across North America, LATAM and APAC, correlating signals in real time from our follow-the-sun analyst team headquartered in Hallandale Beach, FL.
From regional channel partners to publicly-listed mid-market enterprises.
A week is 168 hours. Your analyst covers 40. That is the gap attackers work in.
Round-the-clock coverage takes more than four full-time analysts before anyone books a holiday, which is why most teams buy the tooling and stop there. The alerts still fire at 3am. Nobody is there to act on them. We are, and we do it under your brand.
Alert overload, not security
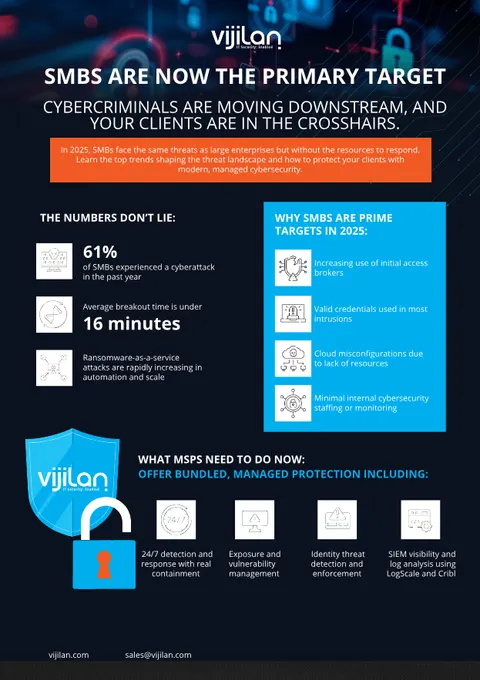
Tools generate thousands of alerts a day. Without analysts triaging them, real attacks slip through the noise.
The hire you can't make
A senior SOC analyst costs $180k+, and you'd need at least four to cover nights, weekends and holidays.
Compliance is non-negotiable
Clients ask for SOC 2, HIPAA, CMMC, PCI evidence. You need real reporting and audit-ready response, not a checkbox.
One hub. Every signal.
Engineered for scale.
The Vijilan Information Security Hub (ViSH) sits on top of CrowdStrike® Falcon Next-Gen SIEM with Cribl Stream pipelines, correlating telemetry from every layer of your clients' stack, in real time.
From raw telemetry to remediated incident
Vendor-agnostic by design
100+ connectors out of the box: CrowdStrike, SentinelOne, Defender, Carbon Black, Sophos, Fortinet, Palo Alto, Cisco, Okta, Entra ID, AWS, Azure, GCP, ConnectWise, Autotask, Jira and more.
 CrowdStrike
 SentinelOne
 Defender
 Fortinet
 Okta
 ConnectWise+ 100 more
Audit-ready in a click
Scheduled executive reports, compliance evidence packs, customizable client dashboards, all white-labelable.
One team.
Two simple ways to work with us.
ThreatRespond™
We add our 24/7 SOC on top of the security tools you already run. We monitor, hunt, investigate, and take action with ThreatContain™. No rip and replace, no starting over.
- →24/7 monitoring across endpoint, identity, network, cloud, app, and data
- →ThreatContain™: real action on threats. We isolate hosts, disable accounts, and block bad traffic.
- →ThreatHunt™ included: we go looking for threats before they strike, mapped to MITRE ATT&CK
- →Works with the security tools you already run, from the top names in the industry
ThreatDefend™
We bring the security tools and run them for you, fully managed by our SOC from day one. Endpoints isolated, accounts shut down, attacks stopped, before your phone rings.
- Everything in ThreatRespond™, including ThreatHunt™
- Real action on threats: host isolation, account shut down, token revoke, process kill
- Built on CrowdStrike Falcon for detection and response (identity, discover, spotlight)
- Falcon Adversary OverWatch managed threat hunting included
- We own the full incident, from root cause to the final report
Six domains.
Zero blind spots.
True mXDR means we don't just watch endpoints. We watch the whole attack surface, and correlate signals that single-tool MDR providers miss.
Works with everything
you already run.
ThreatRespond™ monitors anything an organization can have. If it produces a log, we watch it, correlate it and act on it. 100+ connectors out of the box, including the PSA tools your service desk lives in.


 Microsoft Entra ID

 Microsoft Azure
 CloudTrail
 Defender for Cloud


 Onum
 Carbon Black


 Azure AD Logs
 Microsoft 365


 Autotask



We move you to CrowdStrike Falcon Next-Gen SIEM, with a clean cutover.
Content translation, parallel run, and decommissioning, handled by engineers who have done it dozens of times.


Special care,
by design.
We keep our circle small on purpose. That is how every organization we protect gets our full attention and our best people. Some come to us directly. Some come with a trusted partner at their side. Either way, you get the same white glove care and the same team that never sleeps.
This is the queue.
Somebody is always in it.
An illustration of the incident categories the Vijilan SOC works through, not a live feed. Client telemetry does not go on a marketing page, anonymized or otherwise, which is the same answer you should want when the client being discussed is you.
Real clients and MSP partners,
in their own words.
Every quote is verbatim from a published Vijilan case study. Named clients and partners are published with their review and approval; the rest are anonymized.
"The implementation process was painless, and the support from Vijilan has been outstanding. We now have the visibility and control we need to protect our infrastructure. I highly recommend Vijilan to any organization looking to enhance their cybersecurity."
"Having those capabilities integrated into a single platform has simplified operations, improved our security posture, and allowed us to focus on strategic initiatives rather than day-to-day monitoring and management."
"Vijilan's team functions as a seamless extension of our own. Their ability to manage our data with Cribl and provide active remediation has freed up my internal resources to focus on bigger picture risks. It's a true force multiplier."
"Vijilan takes our problems on as their own. They care about our clients the same way we do, and that level of attention and trust makes all the difference."
"Vijilan's stability and innovation give us the confidence to grow alongside them. They're more than a vendor—they're a true partner."
"Integrating Vijilan's ThreatDefend transformed our managed security practice. We grew revenue quickly, cut alert noise dramatically, and improved our team's efficiency and morale. Vijilan is now a cornerstone of our growth strategy."
Vijilan against the field,
with the receipts.
We publish the full capability matrix rather than a scorecard, and every comparison says where the other provider is the better fit.
Mid-market & enterprise
NextDefend™ managed Falcon Next-Gen SIEM and a SOC that acts, against the mainstream MDR and SIEM field.
MSPs serving SMBs
ThreatRespond™ and ThreatDefend™ against the MSP security stack.
Compliance & technology partnerships
 CrowdStrikeGoogle CloudAWS
 MicrosoftCribl
 Corelight
Trusted at the highest standard.
SOC 2 Type II and ISO 27001 certified. CrowdStrike Powered Service Provider. More than 10 years protecting MSPs, MSSPs, and the organizations that count on them.
Do I have to talk to sales to evaluate Vijilan?
How do MSPs see Vijilan pricing?
What is Vijilan Guard?
What happens after I activate?
Will you email me marketing?
Is the SOC really staffed by humans 24/7?
Do you sell directly to businesses?
What does activation cost?
What if I want to talk to someone right now?
Do you replace our existing security stack?
How fast do you actually respond?
Can we white-label everything?
What's the minimum commitment?
Where are your SOC analysts located?
See your exposure before attackers do.
ThreatAssess runs a CrowdStrike-powered external attack surface scan. Give us a domain and we'll show you what an attacker sees, and what we'd shut down. Results within one business day.
See what an attacker sees.
Run a free External Exposure Report on any domain. Passive intelligence only, no active scanning, delivered to your inbox in minutes.
Threat research, buyer guides and an AI agent security guide, no strings on the open ones.
Ready for a security team
that actually takes action?
Let's talk about where you want to take your business, and how a premium security team helps you get there faster. Whether you run an MSP, or you lead an organization that needs the very best care, you will talk to real people who treat your security like it is their own. No pressure. Just a real conversation with the team that will protect you.